SalahadinSadikAli
$ cat /etc/passwd | grep security | ethical-hacker
Building secure, scalable applications with modern technologies. Specializing in backend security, penetration testing, and clean architecture.
About Me
Get to know me better
I'm a security-focused backend engineer and ethical hacker based in Adama, Ethiopia. I build production applications with an offensive security mindset meaning I design systems knowing exactly how they could be broken, and I harden them before anyone else gets the chance.
Beyond engineering, I actively compete in CTF competitions across HackTheBox, TryHackMe, CTFzone, PicoCTF, and PwnBox. As a member of the Cybersecurity Division at ASTU's CSEC club, I collaborate on security research, awareness initiatives, and technical training with fellow students who share my obsession with secure systems.
I'm currently pursuing a B.Sc. in Software Engineering at Adama Science and Technology University, where I'm developing my skills and passion for building clean, secure, and reliable applications that deliver a great user experience.
I focus on building secure, scalable backend systems and well-structured application architectures. My approach emphasizes clean code, efficient data management, and maintainable solutions designed to handle real-world challenges.
I build efficient web applications with a strong focus on backend performance, clean architecture, and seamless integration. For mobile development, I use Flutter to create reliable cross-platform applications for Android and iOS, backed by well-designed systems.
I'm continuously refining my skills, exploring emerging technologies, and seeking opportunities to collaborate on meaningful and innovative projects.
// quick_facts
Toolchain & Expertise
Technologies and tools I use across the full stack, with a focus on security.
<languages>
<frontend>
<backend>
<databases>
<security>
<tools & practices>
Experience
My professional journey
Freelance Backend Engineer
Self-Employed
Remote
- Delivered production web applications for real clients including MFMGC (Miraj Abubakar General Contractor) and IBSA (electrical company), covering the full project lifecycle from requirements to deployment.
- Built MFMGC company website using React, Vite, FastAPI, and PostgreSQL, deployed on Render and Vercel with SPA routing, CORS configuration, and environment variable management.
- Built IBSA company website using React, Vite, Tailwind CSS, and Sanity CMS, resolving peer dependency conflicts and configuring production deployment pipelines.
- Managed client communication, technical documentation, and iterative delivery across both projects.
Penetration Tester (Internal Audit)
COEC Platform
Adama, Ethiopia
- Conducted an authorized internal security review of the COEC web platform (Node.js/Prisma backend), identifying five critical vulnerabilities including an unauthenticated /api/staff endpoint exposing PII.
- Identified JWT implementation flaws: embedded permissions with no expiry claims, enabling privilege escalation and token replay attacks.
- Produced a formal penetration test report documenting findings, CVSS severity ratings, and remediation recommendations.
Cybersecurity Division Member
CSEC Club — ASTU
Adama, Ethiopia
- Participated in workshops and projects focused on developing and testing secure systems.
- Engaged in CTF competitions across HackTheBox (University CTF / Yekolo Temari), CTFzone, PicoCTF, PwnBox, and TryHackMe covering web exploitation, binary exploitation, and forensics.
- Practiced web attack techniques including LFI with double URL encoding, SQL injection, IDOR enumeration, and WAF bypass methods.
- Performed binary exploitation including checksec analysis and shellcode injection on 32-bit binaries with no stack canary or PIE.
Projects
Selected work and case studies
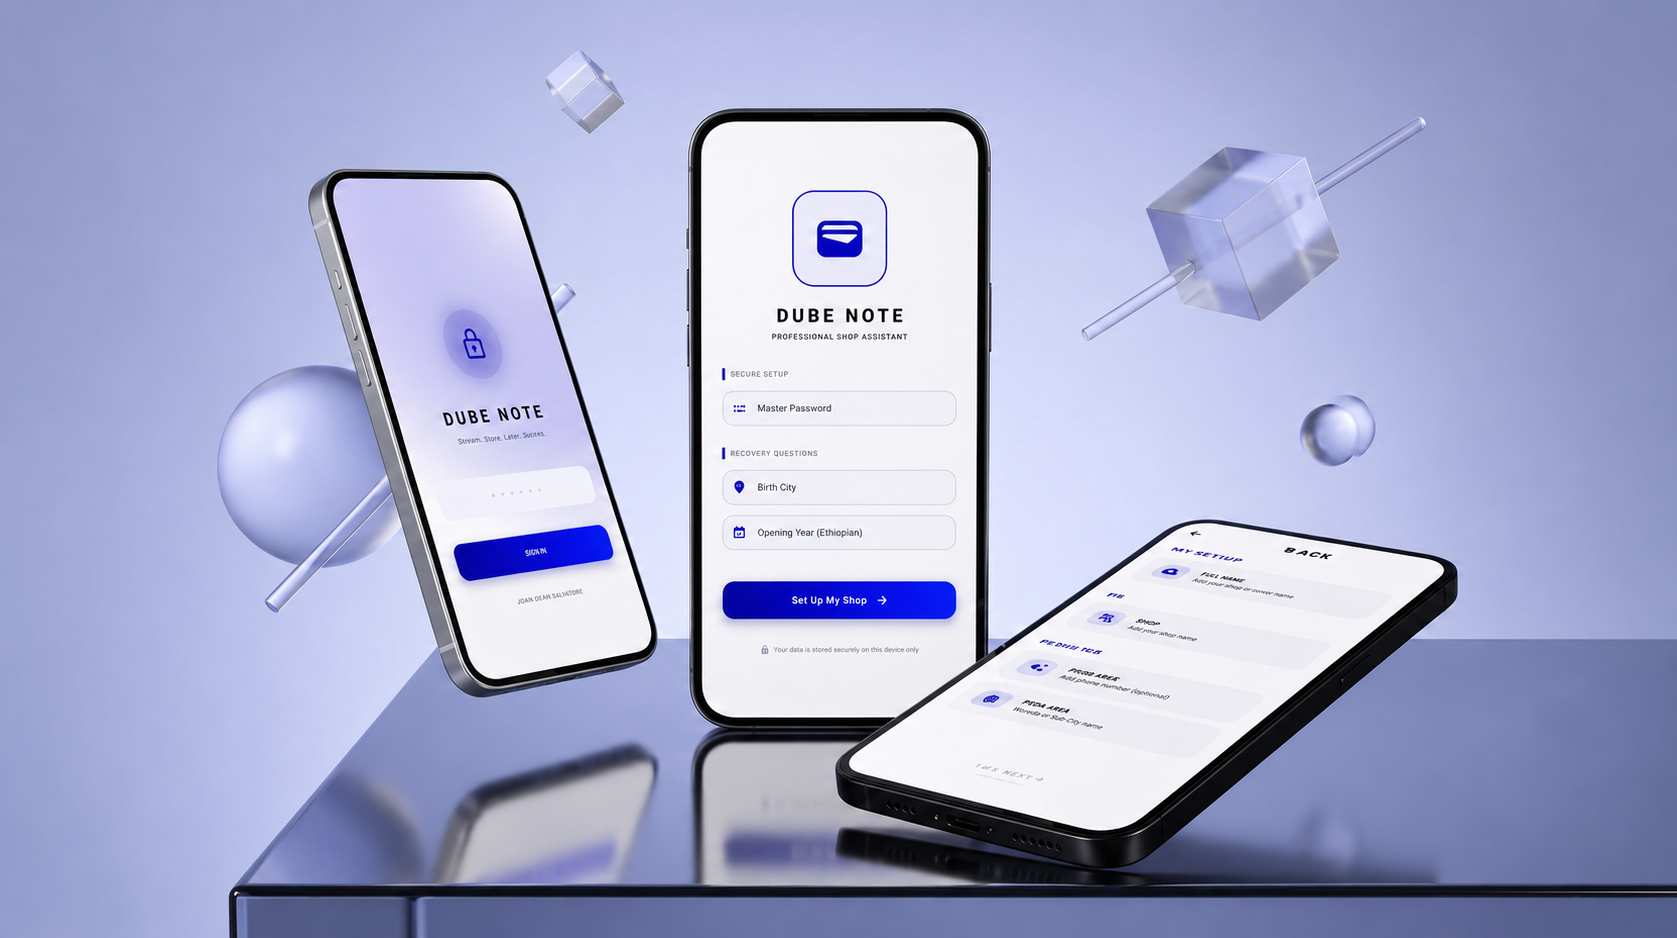
DubeNote
Offline-first credit tracking application for informal shop owners in Ethiopia. Supports Amharic, Afan Oromo, and English.
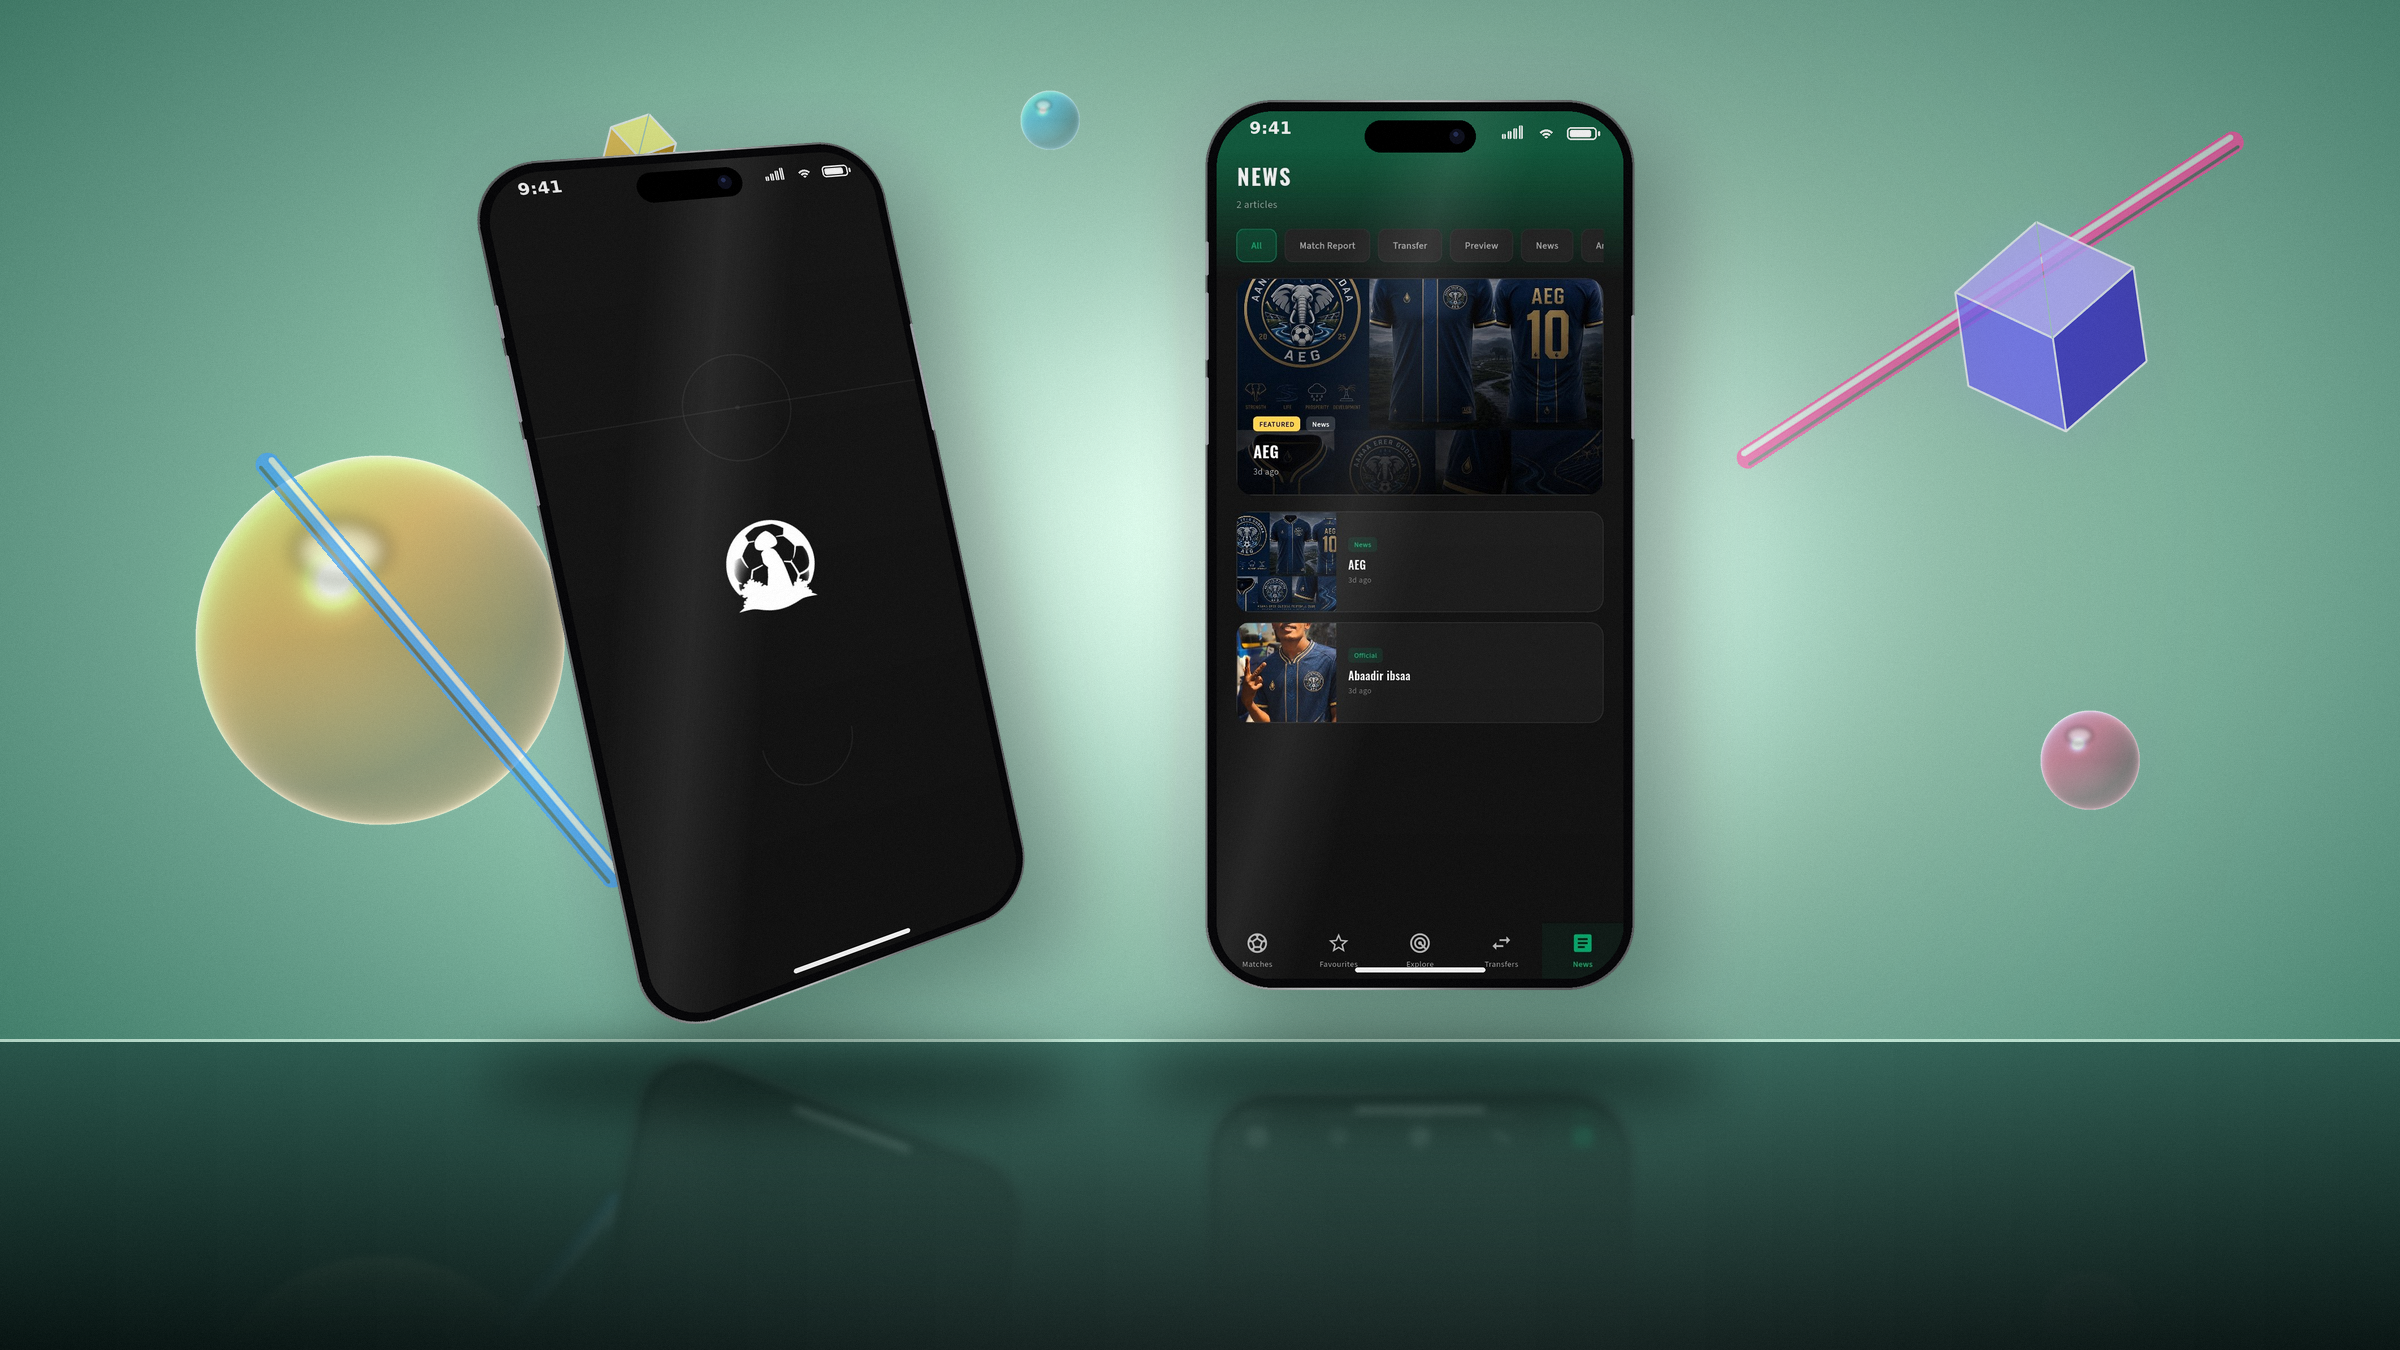
Babile Sport
Full-stack football live-score platform with three integrated apps: a real-time API, an admin broadcast dashboard, and a cross-platform Flutter client.
Babile Sport is a full-stack football live-score and news platform for Babile Zone, Ethiopia, built as three integrated applications. The backend is a FastAPI service (Python 3.12, PostgreSQL, Redis) with a clean layered architecture — routers, services, repositories, models, and schemas — using SQLAlchemy 2.0 async, asyncpg, and Pydantic v2 validation, with JWT RBAC protecting all writes and public reads requiring no auth. A real-time pipeline publishes every create/update to Redis pub/sub and fans out instantly to clients over SSE, with broadcast failures never blocking data entry and offline event queuing with batch replay. The admin dashboard (Next.js 16 App Router, React 19, TypeScript, Tailwind) includes a live match control console for broadcasting scores, period shifts, and events (goals, cards, substitutions), plus full CRUD for clubs, teams, competitions, leagues, news, and players. The mobile client (Flutter/Dart) delivers a BeSoccer-style live-score experience across Android, iOS, Web, and Desktop from a single codebase, receiving real-time updates via SSE with configuration via --dart-define at build time.
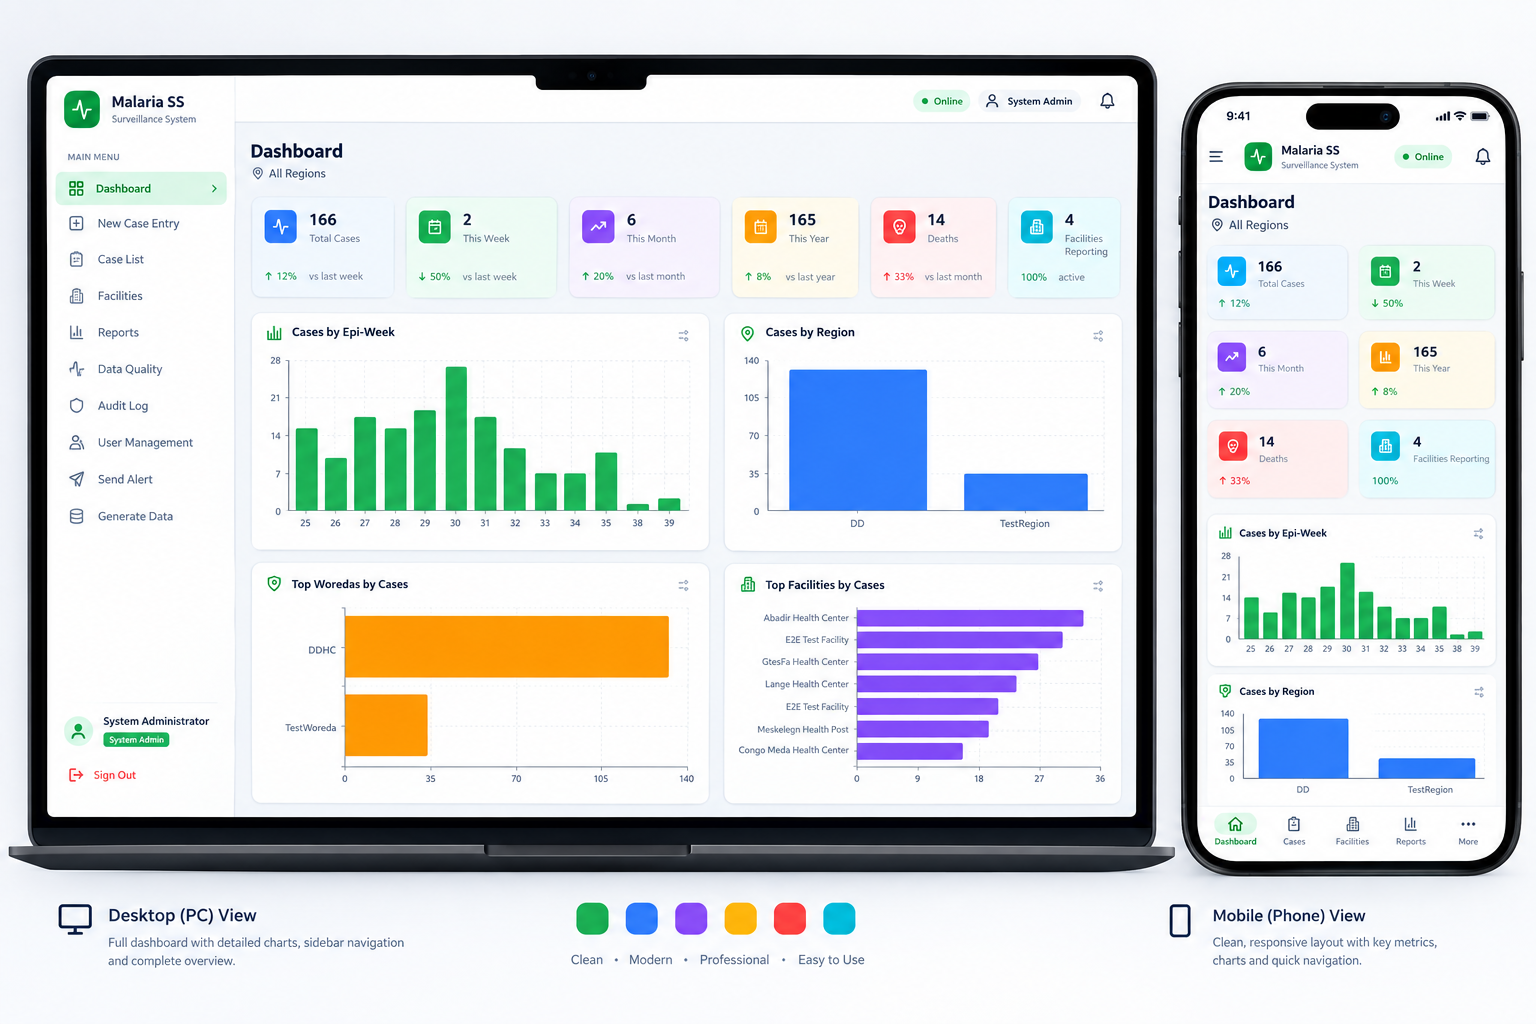
Malaria Surveillance System
Offline-first PWA for malaria case surveillance across Ethiopia’s health system — 6-level RBAC, geographic data scoping, and automatic sync for rural facilities.
A full-stack Progressive Web Application for malaria line-list data collection, surveillance, analytics, and reporting across Ethiopia’s administrative hierarchy (Region → Zone → Woreda → Facility), digitizing paper-based reporting for 7+ health facilities. The frontend (React 18, TypeScript, Vite) uses Zustand for state, Tailwind + shadcn/ui for the interface, Recharts for 8 interactive dashboard charts, and Dexie (IndexedDB) with a Service Worker for full offline entry that syncs automatically on reconnect. The Express.js backend implements JWT auth with bcrypt, a 6-level RBAC hierarchy with geographic data scoping enforced at the SQL layer, a dual-dialect abstraction supporting both SQLite (dev) and PostgreSQL (prod), 3-tier rate limiting, and complete audit logging. Solved key engineering challenges including offline conflict resolution via client-side UUIDs with last-write-wins semantics, per-user API cache isolation using JWT hashes to prevent cross-user data leakage on shared devices, and dialect-aware SQL for placeholder and date-function differences. Includes 5 automated report types with Excel export via SheetJS, data quality monitoring, death-case alerts, and 61 unit tests covering auth, RBAC, and validation, with full Docker/PM2/Nginx deployment documentation.
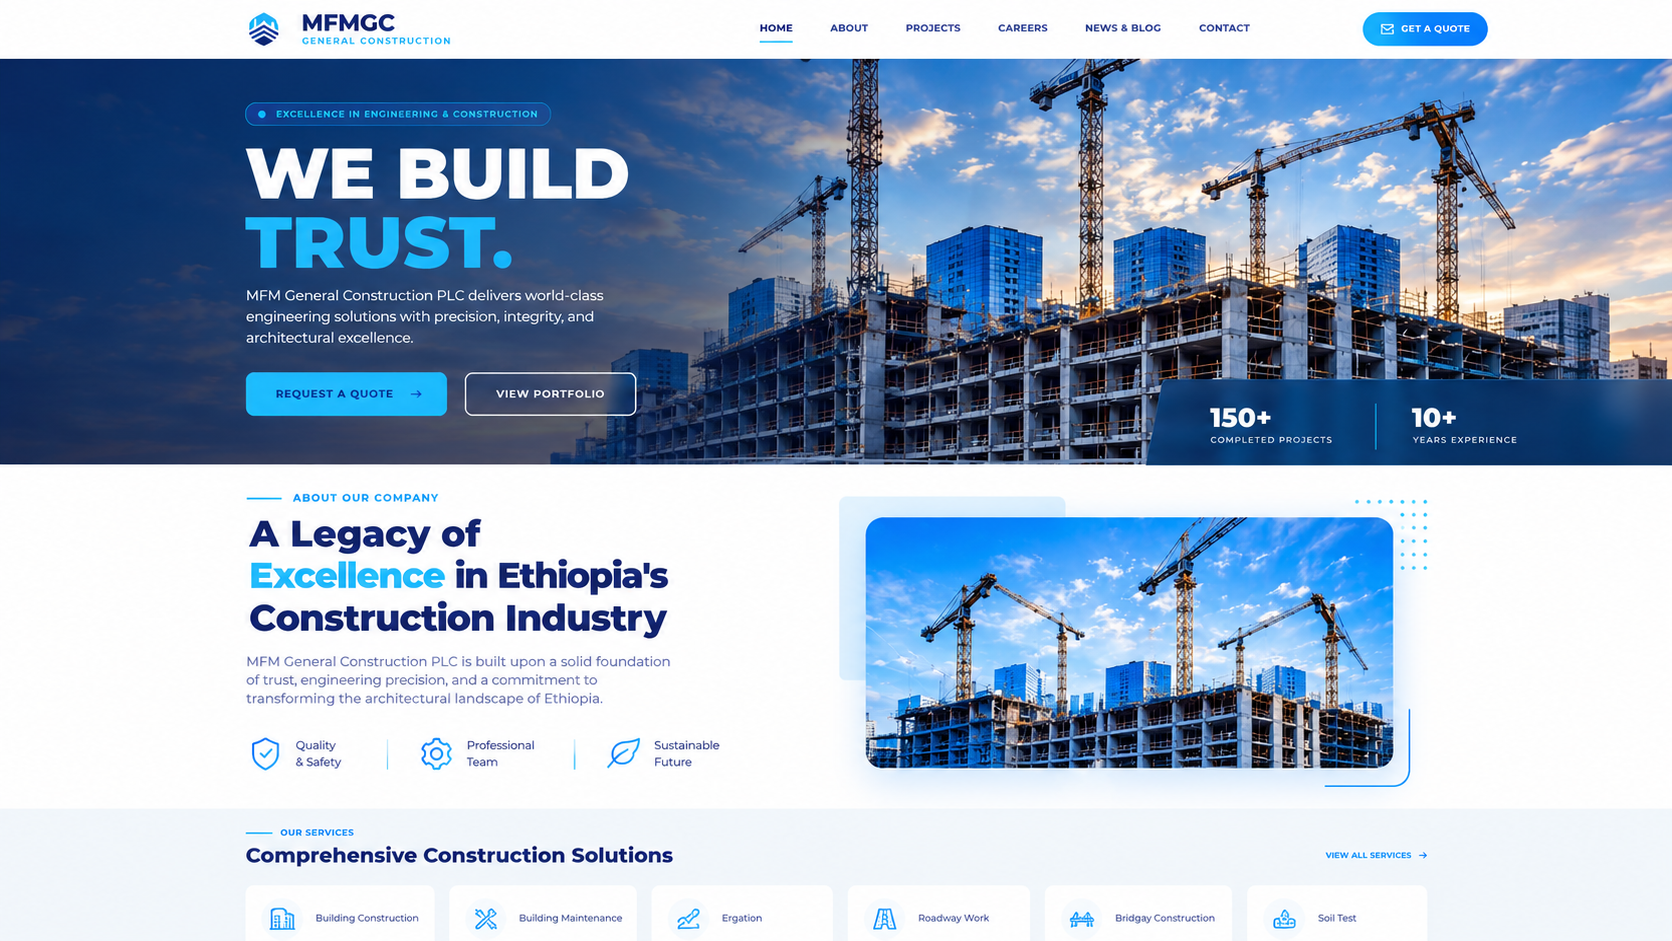
MFMGC
Full production website for a general contractor, built with React, Vite, FastAPI, and PostgreSQL. Deployed on Render and Vercel.
Full production website for MFMGC (Miraj Abubakar General Contractor), covering the full project lifecycle from requirements to deployment. Built with React, Vite, FastAPI, and PostgreSQL, deployed on Render (backend) and Vercel (frontend) with environment-baked Vite config, SPA routing, CORS-hardened API, and environment variable management.
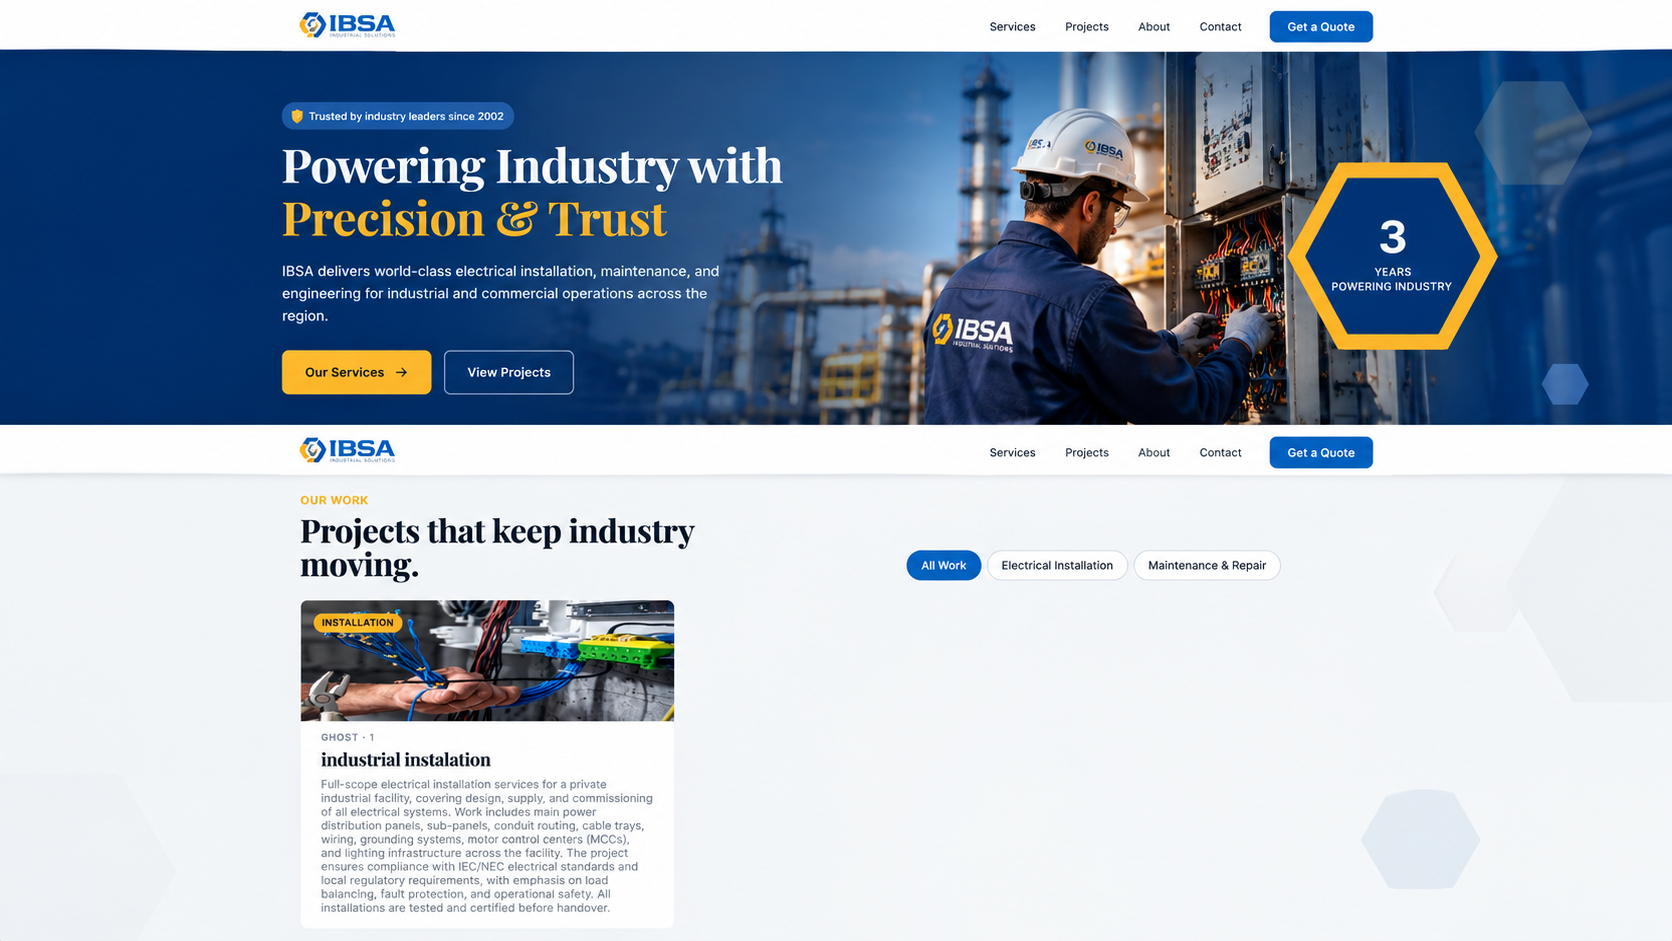
IBSA
Production website for an electrical company using headless CMS architecture with Sanity and frontend deployed on Vercel.
Production website for IBSA, an electrical company, built with React, Vite, Tailwind CSS, and Sanity CMS. Uses headless CMS architecture with content managed via Sanity, resolved peer dependency conflicts during setup, and configured production deployment pipelines with the frontend deployed on Vercel.
Home Service Marketplace
In-progress platform connecting consumers with service providers. Features microkernel architecture and Tesseract OCR for Ethiopian ID verification.
In-progress platform connecting consumers with service providers, built on a microkernel-architecture backend with isolated plugins communicating via an event bus. Implemented production OCR using Tesseract for Ethiopian ID verification with custom format support. Designing separate consumer and provider plugin systems with role-based access control and event-driven communication.
Security Work
Vulnerability research, CTFs, and security tooling
COEC Platform Security Audit
<target> Node.js / SQLAlchemy / PostgreSQL — Production REST API </target>
// Problem
The COEC platform, a production financial technology application, had not undergone a formal security review. As part of an internal audit engagement, I was tasked with identifying vulnerabilities that could compromise user data or system integrity.
// Approach
I performed a white-box penetration test combining automated scanning (Burp Suite, SQLMap) with manual testing for OWASP Top 10 vulnerabilities, logic flaws, and authentication/authorization bypasses. The audit focused on the public-facing API surface and authenticated endpoints.
// Findings
Unauthenticated PII Exposure via /api/staff
The /api/staff endpoint exposed full staff profiles including national IDs, phone numbers, and salary data without authentication.
JWT Privilege Escalation
JWT implementation flaws: permissions embedded directly in the token payload with no expiry claims, enabling privilege escalation and token replay attacks.
SQL Injection in User Search Endpoint
User search parameters were concatenated directly into raw SQL queries without parameterized input, allowing database extraction.
Insecure Direct Object Reference (IDOR)
Transaction records were accessible by incrementing numeric IDs in API endpoints without ownership verification.
Missing Rate Limiting on Auth Endpoints
Login and password reset endpoints lacked rate limiting, enabling brute-force credential attacks.
// Impact
All findings were documented in a formal security report with CVSS 3.1 ratings, proof-of-concept payloads, and prioritized remediation steps. The client patched all critical and high-severity findings within two weeks of report delivery.
Competitive Security
Active platforms where I train, compete, and sharpen offensive security skills through capture-the-flag challenges.
Academic Background
B.Sc. in Software Engineering at Adama Science and Technology University.
B.Sc. in Software Engineering
Adama Science and Technology University (ASTU)
// focus_areas
Get In Touch
Looking for a security-minded developer? Let's talk.